Researcher Claims First Nintendo Switch 2 Jailbreak
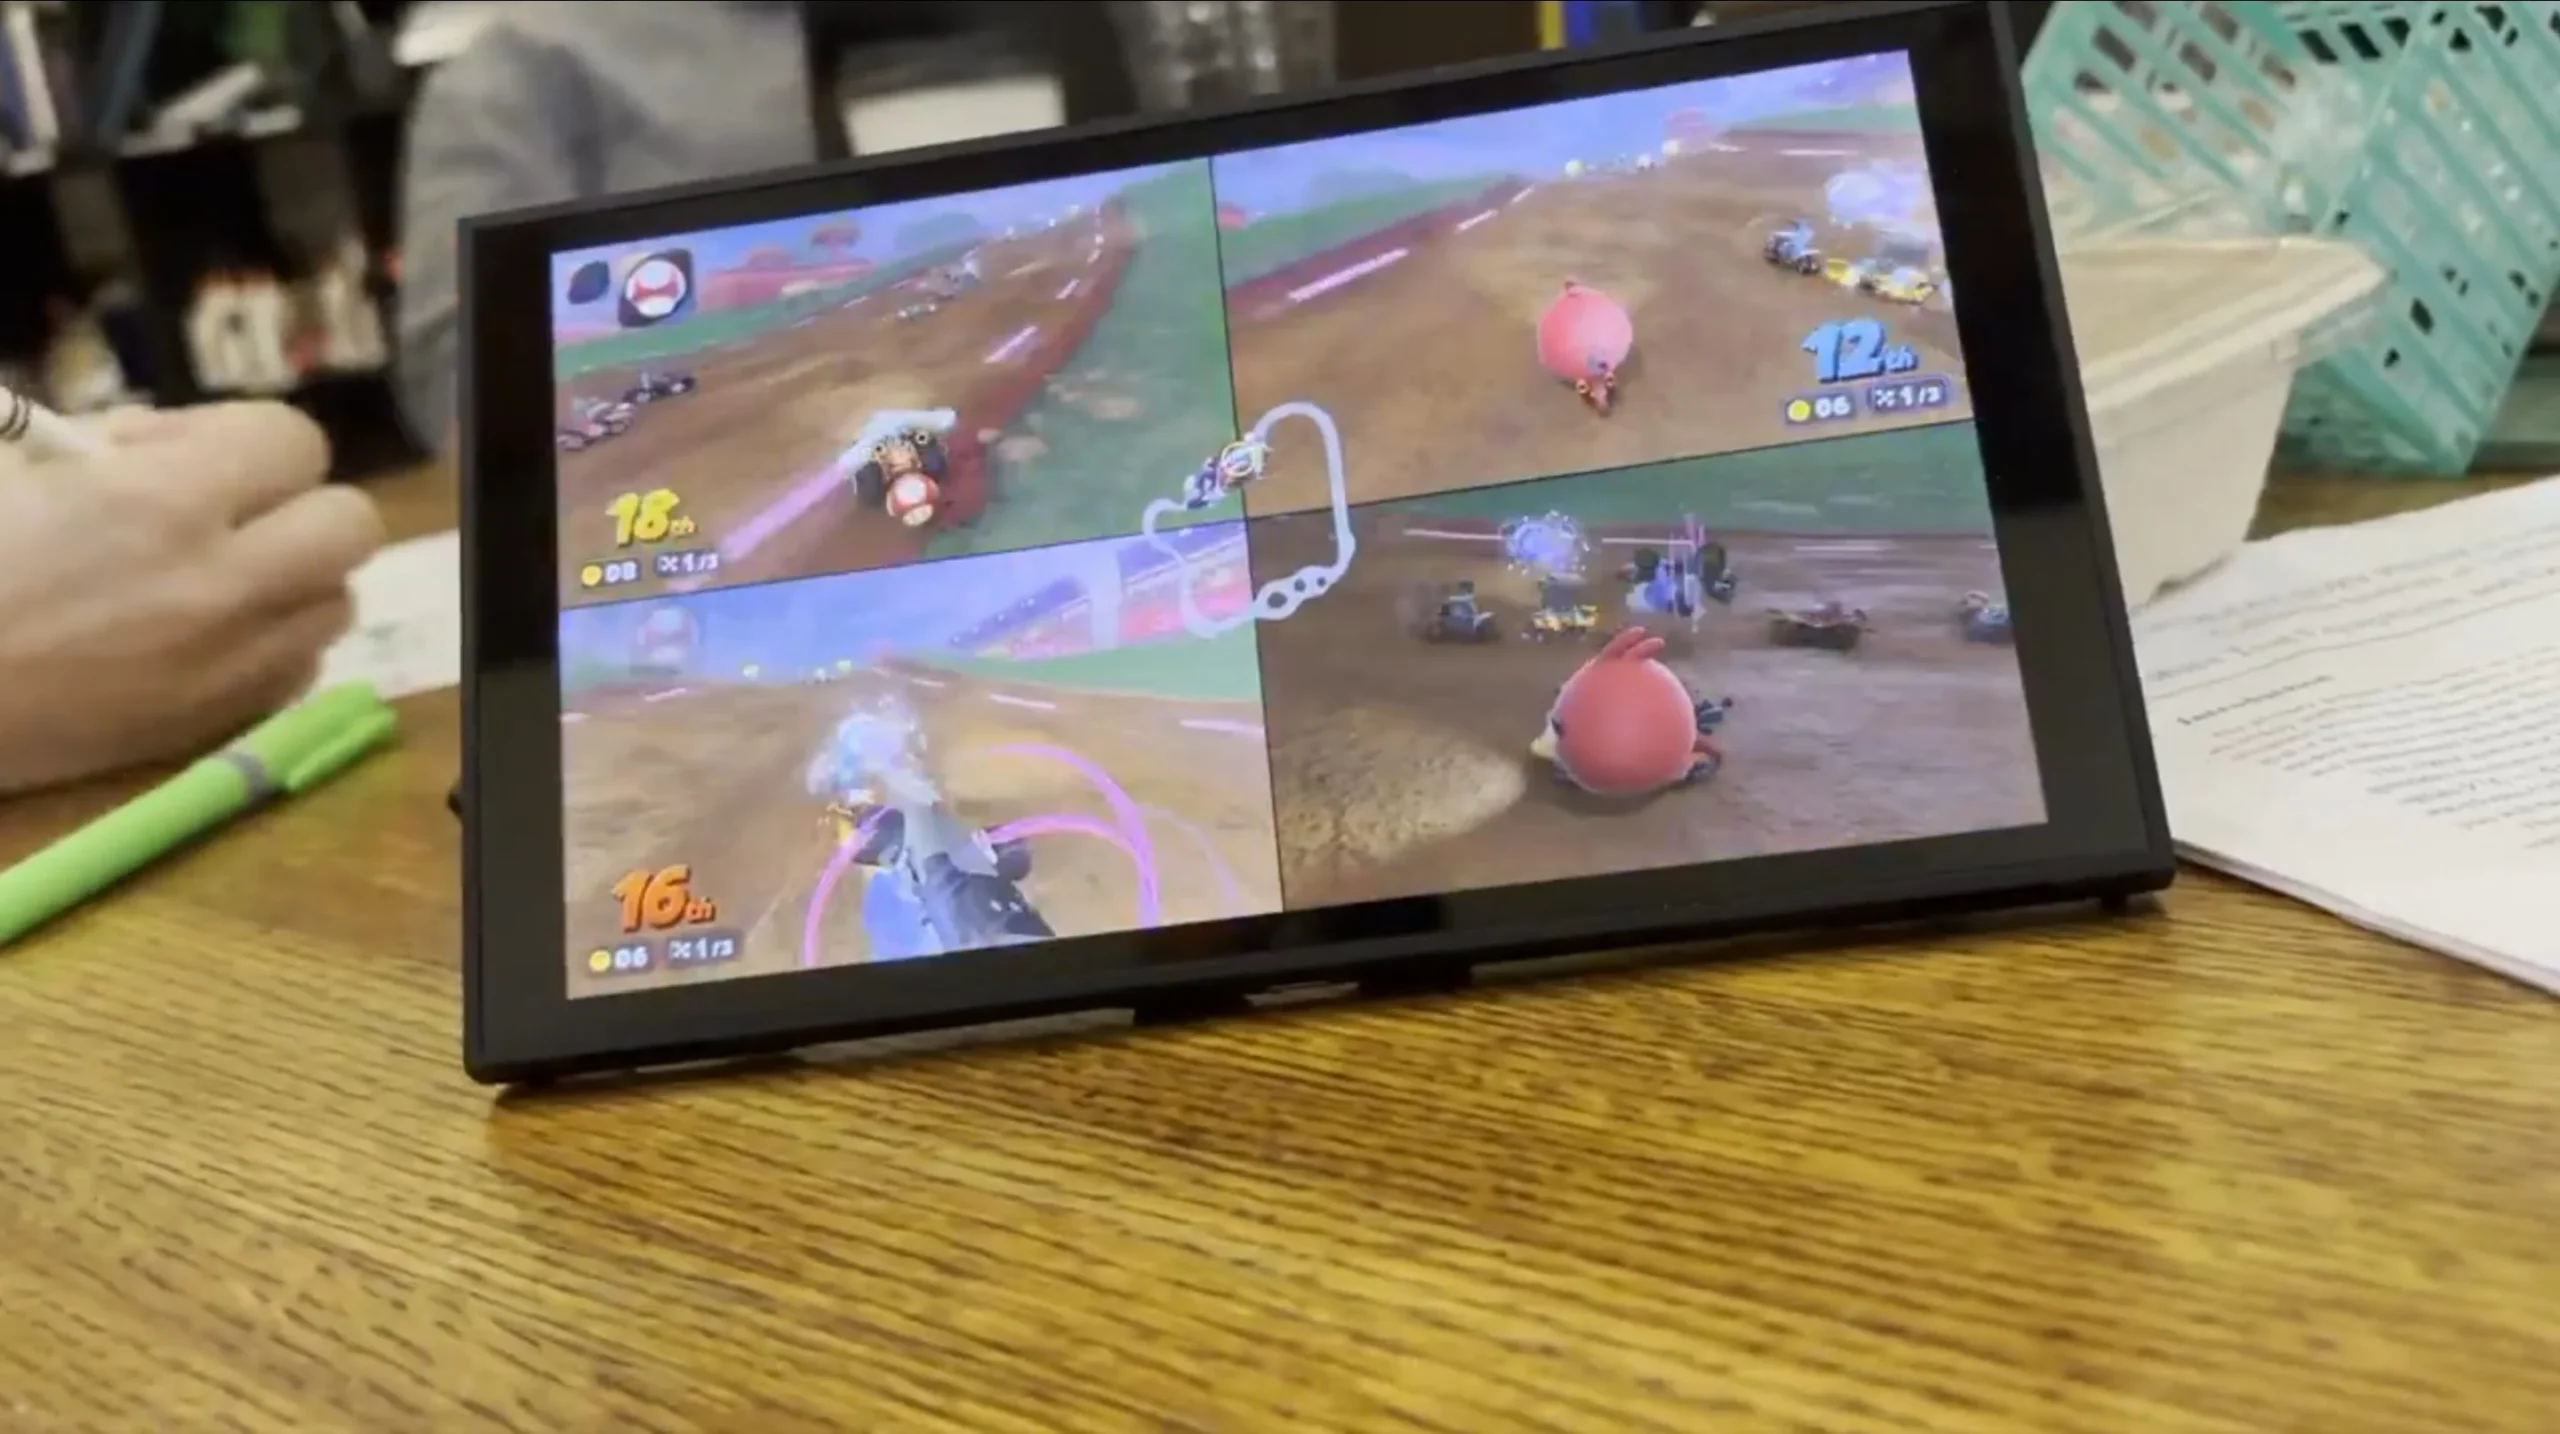
Security researcher Sammy Hajhamid, known online as pepsipu, has claimed the first software-based jailbreak for the Nintendo Switch 2 console running firmware version 23.0.1. Announced on 22 October 2026, the exploit, named NS2JB, operates without hardware modifications and relies on vulnerabilities identified using OpenAI Codex. For console owners in Malaysia tracking system integrity, the development demonstrates the feasibility of third-party code execution, though it remains tethered to a personal computer and lacks full operating system control. Nintendo has not yet issued a patch.
Key Facts
The following table details the verified technical specifications, software dependencies, and release channels associated with the initial Nintendo Switch 2 tethered jailbreak. Documented by researcher Sammy Hajhamid in October 2026, the exploit targets firmware 23.0.1 without requiring physical hardware modifications.
The NS2JB exploit represents the first reported software-based tethered jailbreak targeting Nintendo Switch 2 firmware 23.0.1.
| Attribute | Value |
| Target Hardware | Nintendo Switch 2 |
| Vulnerable Firmware | Version 23.0.1 |
| Exploit Designation | NS2JB (ns2jb) |
| Exploit Architecture | Software-only, tethered |
| Vector Source | SmileBASIC application vulnerability |
| Vulnerability Analysis Tool | OpenAI Codex |
| Lead Developer | Sammy Hajhamid (pepsipu) |
| Announcement Date | 22 October 2026 |
| Source Code Repository | GitLab |
How Does the NS2JB Switch 2 Exploit Work?
NS2JB functions as a software-only, tethered jailbreak that targets security flaws in SmileBASIC, a programming application originally released for the original Nintendo Switch. By leveraging vulnerabilities discovered with the assistance of OpenAI Codex, the exploit executes arbitrary native code within the Switch 2 operating system without requiring physical hardware modifications or soldered modchips.
According to Hajhamid, the exploit grants execution privileges as standard system modules and the built-in file system sysmodule. This access level permits users to run homebrew software, reverse engineer native Switch 2 games, export saved data, and control console peripherals through memory-mapped input/output (MMIO). To demonstrate code execution, the developer introduced custom avatar assets—including Hatsune Miku, Peter Griffin, and Cinnamoroll—into the Switch 2 exclusive title Mario Kart World.
“ns2jb is a software-only, tethered jailbreak for the Switch 2. It allows running arbitrary native code as any ordinary sysmodule, and as the built-in fs sysmodule. This lets us run homebrew, reverse engineer and mod Switch 2 games, back up save files off the Switch, and access most of the Switch 2’s peripherals through MMIO. To my knowledge, it’s the first such exploit for the Switch 2.”
— Sammy Hajhamid (pepsipu)
The NS2JB tool achieves arbitrary code execution through an unpatched legacy application rather than direct hardware tampering.
What Are the Limitations of the NS2JB Jailbreak?
The NS2JB jailbreak is tethered, meaning the Nintendo Switch 2 must connect to an external computer to trigger the exploit upon every console restart. It does not provide total control over the operating system, leaving the system software partially restricted rather than fully unlocked for persistent standalone execution.
Because the exploit relies on security holes present in firmware 23.0.1, standard over-the-air system updates from Nintendo can eliminate the vector. Furthermore, the mandatory computer tether restricts portable utility, as restarting the handheld outside a tethered workstation returns the system to factory operation. Hajhamid has uploaded the codebase and deployment steps to GitLab for independent scrutiny by security analysts and homebrew enthusiasts.
Console reboots reset the Nintendo Switch 2 to its standard state, requiring a persistent computer link to reinitialise the jailbreak.
What It Means for Malaysian Buyers
For gamers and prospective buyers in Malaysia, the NS2JB exploit does not alter official retail availability, pricing, or local warranty conditions for the Nintendo Switch 2. Official Malaysian distributors have announced no hardware revisions, and applying third-party exploits carries inherent risks of software bricking and immediate invalidation of local warranty support.
The source documentation does not list official Malaysian pricing, release schedules, or local distributor allocations for the console. While imported units or early inventory may arrive running firmware 23.0.1, executing unofficial code risks permanent service bans across Nintendo Network infrastructure. Local consumers looking for standard consumer use should note that untethered, persistent exploits do not currently exist for the platform.
Executing tethered homebrew exploits risks voiding official distributor warranty cover and forfeiting access to networked gaming services in Malaysia.
Common Questions
This section answers the primary operational questions regarding the NS2JB Nintendo Switch 2 exploit, covering hardware prerequisites, post-reboot persistence, and artificial intelligence involvement. These responses address technical safety, system capabilities, and practical limitations based directly on public disclosures released by security researcher Sammy Hajhamid.
Practical deployment of NS2JB remains confined to tethered environments and experimental homebrew testing rather than permanent consumer modification.
Does the NS2JB exploit require physical modchips?
No, NS2JB is an entirely software-based exploit that does not require opening the console casing or installing hardware modchips. It operates by exploiting memory flaws in the SmileBASIC application to execute native code tethered through an external computer connection.
Can the Switch 2 stay jailbroken after a reboot?
No, the jailbreak is tethered and non-persistent across power cycles. Whenever the Nintendo Switch 2 restarts or shuts down completely, the system returns to its factory state, requiring the user to reconnect the console to a computer to reactivate the exploit.
Did artificial intelligence generate the jailbreak exploit?
OpenAI Codex did not write the exploit autonomously, but the researcher used the artificial intelligence tool to locate security vulnerabilities in SmileBASIC. Sammy Hajhamid then used those AI-assisted findings to develop and compile the working NS2JB codebase published on GitLab.
Sources and Methodology
This report synthesises technical disclosure documentation and claims published by security researcher Sammy Hajhamid on X and GitLab, cross-referenced with reporting by Lowyat.NET on 23 October 2026. Editorial verification evaluates software security mechanisms against disclosed technical documentation. The source material contains no retail pricing figures or foreign currency estimates to convert.
Technical assessments reflect developer disclosures published on 22 and 23 October 2026 across GitLab, X, and independent reporting.
Related coverage
More AI & Software →Filed under
- #Tech
- #Nintendo
Network · latest from sister sites